Wednesday, May 4, 2011

Get Rid of Trojan.Win32.buzus.hhle and undo the damage related

Being true to its name, the trojan disorders computer system so that it starts producing buzzing and creaking sounds. It overheats RAM memory to critical point. Worst case is when outdated or disordered computers do not automatically switch off, if critical RAM temperature is detected. Such computers may physically collapse as their memory is burnt due to overheating.
However, that is a side-effect of the trojan presence as its main task is to establish a connection to remote server. However, the trojan has been developed so awkwardly that it often destroys or badly disorders computer systems  while executing its task.
To get rid of  Trojan.Win32.buzus.hhle is an urgent measure, for the threat belongs to the category of infections of extremely destructive behavior. Click here to start Trojan.win32.buzus.hhle removal and undo the damage it has already caused.


Trojan.Win32.Buzus variants:
Trojan.Win32.Buzus.anee
Trojan.Win32.Buzus.arqx
Trojan.Win32.Buzus.abq
Trojan.win32.buzus.hhle

Trojan.win32.buzus.hhle removal tool:


Remove Antivirrt.com agents and rogue product from the website

Antivirrt.com  is a necessary components of adware propagation. The website is either visited by users as a result of their webs-surfing re-routing or there is internal infections forcing web-browser of a compromised PC to open this page. Other types of inner PC infections connect to the concealed page of this website and enable it to find system vulnerabilities to drop the adware in a hidden mode.
Get rid of Antivirrt.com infections and do not visit this page and in no way keep it open. Removal of Antivirrt.com infections may include the adware deletion, as well as extermination of infections aimed at  downloading or enticing users to download, the adware in question. Relevant remedy to fix the issue is available here.

Antivirrt.com screenshot:


Antivirrt.com removal tool:


Tuesday, May 3, 2011

Remove XP Internet Security and isolate your PC from viruses

XP Internet Security is going to isolate compromised computer system bit by bit. As a consequence, you should not postpone XP Internet Security removal, if applicable.
The isolation means that a compromised PC will be deprived of access to computer networks, including Internet. Access will be denied to software installed, too.
The program is normally identified as adware or rogue antispyware, but it is seems to be more reasonable to consider it as a virus because of its aggressive behavior and impact on compromised computers.
In order to get rid of XP Internet Security virus  at the latest stages of its development, you need to reboot in Safe Mode for manual adware deletion and in Safe Mode with Networking to delete the virus by appropriate antivirus.
Click here to upload free scanner of recommended antivirus that has been found capable of deleting any adware, including XP Internet Security in its most aggressive states.

XP Internet Security screenshot:


XP Internet Security remover:


XP Internet Security manual removal guide:
Delete infected files:
%UserProfile%\AppData\Local\pw.exe
%UserProfile%\AppData\Local\MSASCui.exe
%UserProfile%\Local Settings\Application Data\pw.exe
%UserProfile%\Local Settings\Application Data\MSASCui.exe
Delete infected registry entries:
HKEY_CURRENT_USER\Software\Classes\pezfile
HKEY_CLASSES_ROOT\pezfile
HKEY_CURRENT_USER\Software\Classes\.exe\shell\open\command "(Default)" = "%UserProfile%\Local Settings\Application Data\pw.exe" /START "%1" %*
HKEY_CURRENT_USER\Software\Classes\pezfile\shell\open\command "(Default)" = "%UserProfile%\Local Settings\Application Data\pw.exe" /START "%1" %*
HKEY_CLASSES_ROOT\.exe\shell\open\command "(Default)" = "%UserProfile%\Local Settings\Application Data\pw.exe" /START "%1" %*
HKEY_CLASSES_ROOT\pezfile\shell\open\command "(Default)" = "%UserProfile%\Local Settings\Application Data\pw.exe" /START "%1" %*
HKEY_LOCAL_MACHINE\SOFTWARE\Clients\StartMenuInternet\FIREFOX.EXE\shell\open\command "(Default)" = "%UserProfile%\Local Settings\Application Data\pw.exe" /START "C:\Program Files\Mozilla Firefox\firefox.exe"
HKEY_LOCAL_MACHINE\SOFTWARE\Clients\StartMenuInternet\FIREFOX.EXE\shell\safemode\command "(Default)" = "%UserProfile%\Local Settings\Application Data\pw.exe" /START "C:\Program Files\Mozilla Firefox\firefox.exe" -safe-mode
HKEY_LOCAL_MACHINE\SOFTWARE\Clients\StartMenuInternet\IEXPLORE.EXE\shell\open\command "(Default)" = "%UserProfile%\Local Settings\Application Data\pw.exe" /START "C:\Program Files\Internet Explorer\iexplore.exe"
HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Security Center "AntiVirusOverride" = "1"
HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Security Center "FirewallOverride" = "1"

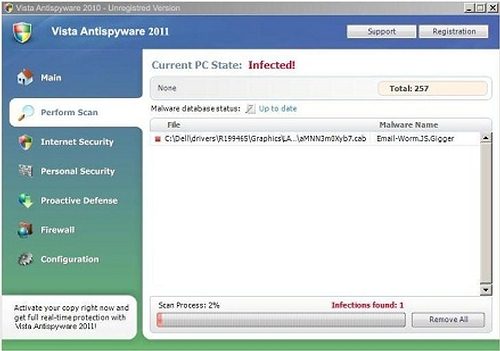
Remove Vista Anti-Spyware 2011 for Your Comfort

The adware does not waste the least opportunity to infect a computer system. That means there are few methods for program distribution yet not used to spread the adware. Establishing what method is more or less common and efficient takes a great research effort that none of experts has had a will to make. However, the program’ behaviors has been properly studied and the conclusion that Vista Anti-Spyware 2011 removal is to be performed  for the sake of user’s privacy and comfort, as well as to avoid quite possible system malfunctioning.  
Click this link to give your PC a free can treatment and get rid of Vista Anti-Spyware 2011 as one of the detected threats.

Vista Anti-Spyware 2011 screesnhot:


Vista Anti-Spyware 2011 remover download:


Vista Anti-Spyware 2011 manual removal guide:
Delete infected files:
%UserProfile%\AppData\Local\pw.exe
%UserProfile%\AppData\Local\MSASCui.exe
%UserProfile%\Local Settings\Application Data\pw.exe
%UserProfile%\Local Settings\Application Data\MSASCui.exe
Delete infected registry entries:
HKEY_CURRENT_USER\Software\Classes\pezfile
HKEY_CLASSES_ROOT\pezfile
HKEY_CURRENT_USER\Software\Classes\.exe\shell\open\command "(Default)" = "%UserProfile%\Local Settings\Application Data\pw.exe" /START "%1" %*
HKEY_CURRENT_USER\Software\Classes\pezfile\shell\open\command "(Default)" = "%UserProfile%\Local Settings\Application Data\pw.exe" /START "%1" %*
HKEY_CLASSES_ROOT\.exe\shell\open\command "(Default)" = "%UserProfile%\Local Settings\Application Data\pw.exe" /START "%1" %*
HKEY_CLASSES_ROOT\pezfile\shell\open\command "(Default)" = "%UserProfile%\Local Settings\Application Data\pw.exe" /START "%1" %*
HKEY_LOCAL_MACHINE\SOFTWARE\Clients\StartMenuInternet\FIREFOX.EXE\shell\open\command "(Default)" = "%UserProfile%\Local Settings\Application Data\pw.exe" /START "C:\Program Files\Mozilla Firefox\firefox.exe"
HKEY_LOCAL_MACHINE\SOFTWARE\Clients\StartMenuInternet\FIREFOX.EXE\shell\safemode\command "(Default)" = "%UserProfile%\Local Settings\Application Data\pw.exe" /START "C:\Program Files\Mozilla Firefox\firefox.exe" -safe-mode
HKEY_LOCAL_MACHINE\SOFTWARE\Clients\StartMenuInternet\IEXPLORE.EXE\shell\open\command "(Default)" = "%UserProfile%\Local Settings\Application Data\pw.exe" /START "C:\Program Files\Internet Explorer\iexplore.exe"
HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Security Center "AntiVirusOverride" = "1"
HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Security Center "FirewallOverride" = "1"

Sunday, May 1, 2011

Remove Win 7 Anti-Virus 2011 Counterfeit and Parasite

The program is a half-counterfeit and a half-parasite.It reports merely invented system problems. That provides a ground for its determination as a counterfeited system improver.
Further on, Win 7 Anti-Virus 2011 comprises totally free scanners that actually detect system problems, but there are two problems in such utilization, luck of authorization of  the free scanners developers and poor quality of such tools. It should be emphasized that the tools  applied by Win 7 Anti-Virus 2011 in violation to their owners rights do not pretends to provide exhausting system protection. They often fail to recognize a good half of threats and in overwhelming majority of cases are useless against  latest releases of computer infections.
If genuine scanners fail do detect adequate number of infections, the adware will add intentional false positives to prove the system is in danger and thus provide a reason for its paid activation.
Even the threats that have been actually detected will not be cured, if you activate the counterfeit.
Get rid of Win 7 Anti-Virus 2011 as inappropriate and illegal software product. Click here to apply best quality free scanner for the purpose of Win 7 Anti-Virus 2011 removal.

Win 7 Anti-Virus 2011 screenshot:


Rogue anti-spyware removal tool:


Win 7 Anti-Virus 2011 manual removal guide:
Delete infected files:
 %UserProfile%\AppData\Local\pw.exe
%UserProfile%\AppData\Local\MSASCui.exe
%UserProfile%\Local Settings\Application Data\pw.exe
%UserProfile%\Local Settings\Application Data\MSASCui.exe

Delete Win 7 Anti-Virus 2011 registry entries:
 HKEY_CURRENT_USER\Software\Classes\pezfile
HKEY_CLASSES_ROOT\pezfile
HKEY_CURRENT_USER\Software\Classes\.exe\shell\open\command "(Default)" = "%UserProfile%\Local Settings\Application Data\pw.exe" /START "%1" %*
HKEY_CURRENT_USER\Software\Classes\pezfile\shell\open\command "(Default)" = "%UserProfile%\Local Settings\Application Data\pw.exe" /START "%1" %*
HKEY_CLASSES_ROOT\.exe\shell\open\command "(Default)" = "%UserProfile%\Local Settings\Application Data\pw.exe" /START "%1" %*
HKEY_CLASSES_ROOT\pezfile\shell\open\command "(Default)" = "%UserProfile%\Local Settings\Application Data\pw.exe" /START "%1" %*
HKEY_LOCAL_MACHINE\SOFTWARE\Clients\StartMenuInternet\FIREFOX.EXE\shell\open\command "(Default)" = "%UserProfile%\Local Settings\Application Data\pw.exe" /START "C:\Program Files\Mozilla Firefox\firefox.exe"
HKEY_LOCAL_MACHINE\SOFTWARE\Clients\StartMenuInternet\FIREFOX.EXE\shell\safemode\command "(Default)" = "%UserProfile%\Local Settings\Application Data\pw.exe" /START "C:\Program Files\Mozilla Firefox\firefox.exe" -safe-mode
HKEY_LOCAL_MACHINE\SOFTWARE\Clients\StartMenuInternet\IEXPLORE.EXE\shell\open\command "(Default)" = "%UserProfile%\Local Settings\Application Data\pw.exe" /START "C:\Program Files\Internet Explorer\iexplore.exe"
HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Security Center "AntiVirusOverride" = "1"
HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Security Center "FirewallOverride" = "1"

Saturday, April 30, 2011

XP Anti-Spyware 2011 Removal for PC Independence

Hackers issue viruses. Many IT experts dedicate themselves to preventing   virus mass-spreading. However, the current solution is a PC specific protection, because the web provides great liberties for swindlers to block viruses before approaching computer systems. PC specific protection means a security solution (antiviris) is to be installed on a PC or else the PC is vulnerable to viruses.
Some of the swindlers have invented other viruses in that connection. XP Anti-Spyware 2011 is one of such recent viruses, which pretend to replace a protection for computer system. However, it should not be confused with a mere fake antivirus.
A fake antivirus is only aimed on faking security solution to be rewarded as though it is providing security services. In case of the rogue in question, the scam goes beyond as the counterfeiting has become a secondary purpose of the adverting infection introduction. The aim is to keep genuine security tools off a compromised machine and thus to turn such machine into a bot governed by remote hackers.
Get rid of XP Anti-Spyware 2011 to prevent your PC from becoming a slave to hackers. XP Anti-Spyware 2011 removal tool and free scanner is ready for download here. The link is ban-protected. If any difficulties occur in the course if using the link, please restart your PC is Safe Mode with Networking (tip for Windows XP users) and try again.

XP Anti-Spyware 2011 screenshot:


XP Anti-Spyware 2011 remover download:


XP Anti-Spyware 2011 manual removal instructions:
Delete infected files:
%UserProfile%\AppData\Local\pw.exe
%UserProfile%\AppData\Local\MSASCui.exe
%UserProfile%\Local Settings\Application Data\pw.exe
%UserProfile%\Local Settings\Application Data\MSASCui.exe
Delete infected registry entries:
HKEY_CURRENT_USER\Software\Classes\pezfile
HKEY_CLASSES_ROOT\pezfile
HKEY_CURRENT_USER\Software\Classes\.exe\shell\open\command "(Default)" = "%UserProfile%\Local Settings\Application Data\pw.exe" /START "%1" %*
HKEY_CURRENT_USER\Software\Classes\pezfile\shell\open\command "(Default)" = "%UserProfile%\Local Settings\Application Data\pw.exe" /START "%1" %*
HKEY_CLASSES_ROOT\.exe\shell\open\command "(Default)" = "%UserProfile%\Local Settings\Application Data\pw.exe" /START "%1" %*
HKEY_CLASSES_ROOT\pezfile\shell\open\command "(Default)" = "%UserProfile%\Local Settings\Application Data\pw.exe" /START "%1" %*
HKEY_LOCAL_MACHINE\SOFTWARE\Clients\StartMenuInternet\FIREFOX.EXE\shell\open\command "(Default)" = "%UserProfile%\Local Settings\Application Data\pw.exe" /START "C:\Program Files\Mozilla Firefox\firefox.exe"
HKEY_LOCAL_MACHINE\SOFTWARE\Clients\StartMenuInternet\FIREFOX.EXE\shell\safemode\command "(Default)" = "%UserProfile%\Local Settings\Application Data\pw.exe" /START "C:\Program Files\Mozilla Firefox\firefox.exe" -safe-mode
HKEY_LOCAL_MACHINE\SOFTWARE\Clients\StartMenuInternet\IEXPLORE.EXE\shell\open\command "(Default)" = "%UserProfile%\Local Settings\Application Data\pw.exe" /START "C:\Program Files\Internet Explorer\iexplore.exe"
HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Security Center "AntiVirusOverride" = "1"
HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Security Center "FirewallOverride" = "1"

Trojan.Win32.Monderb Removal Technology

Trojan.Win32.Monderb is a program written on  C++. It is compatible with Windows and other operating system, with Windows as a primary target.
 The infection is  installed in a way that is referred to by IT experts as obfuscation. Obfuscation implies tricks aimed to conceal the infection and thus to reduce Trojan.Win32.Monderb removal risk.
The trojan in question practices  deletion of its original entry which is dropped into system folder under random name. By the way, random name also proves the intention of the trojan to bewilder  potential Trojan.Win32.Monderb removers.
The original entry is deleted once it succeeds to create subsequent  morph of the trojan. New created version of the trojan  performs a set of destructive actions and tends to migrate, i.e. to change its system address.
Get rid of Trojan.Win32.Monderb in spite of its self-defense tricks, as well as clean your PC of other parasites applying free scanner available here. 

Trojan.Win32.Monderb variants:
Trojan.Win32.Monderb [Ikarus]
Trojan.Win32.Monderb.acke
Trojan.Win32.Monderb.ahoe
Trojan.Win32.Monderb.almg
Trojan.Win32.Monderb.aprm
Trojan.Win32.Monderb.gen
Trojan.Win32.monderb.gjo
Trojan.Win32.Monderb.gjb
Trojan.Win32.Monderb.kuf
Trojan.Win32.Monderb.vwm
Trojan.Win32.Monderb.yek
Trojan.Win32.Monderb.yfa

Trojan.Win32.Monderb remover download: