Tuesday, May 3, 2011

Remove Vista Anti-Spyware 2011 for Your Comfort

The adware does not waste the least opportunity to infect a computer system. That means there are few methods for program distribution yet not used to spread the adware. Establishing what method is more or less common and efficient takes a great research effort that none of experts has had a will to make. However, the program’ behaviors has been properly studied and the conclusion that Vista Anti-Spyware 2011 removal is to be performed  for the sake of user’s privacy and comfort, as well as to avoid quite possible system malfunctioning.  
Click this link to give your PC a free can treatment and get rid of Vista Anti-Spyware 2011 as one of the detected threats.

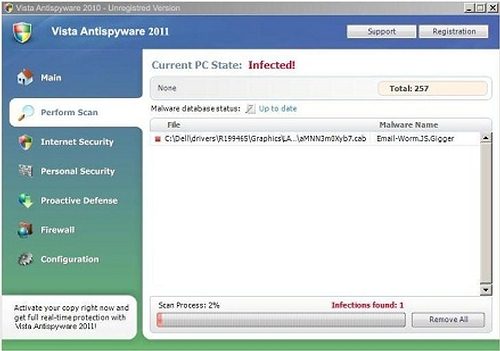
Vista Anti-Spyware 2011 screesnhot:

Vista Anti-Spyware 2011 remover download:


Vista Anti-Spyware 2011 manual removal guide:
Delete infected files:
%UserProfile%\AppData\Local\pw.exe
%UserProfile%\AppData\Local\MSASCui.exe
%UserProfile%\Local Settings\Application Data\pw.exe
%UserProfile%\Local Settings\Application Data\MSASCui.exe
Delete infected registry entries:
HKEY_CURRENT_USER\Software\Classes\pezfile
HKEY_CLASSES_ROOT\pezfile
HKEY_CURRENT_USER\Software\Classes\.exe\shell\open\command "(Default)" = "%UserProfile%\Local Settings\Application Data\pw.exe" /START "%1" %*
HKEY_CURRENT_USER\Software\Classes\pezfile\shell\open\command "(Default)" = "%UserProfile%\Local Settings\Application Data\pw.exe" /START "%1" %*
HKEY_CLASSES_ROOT\.exe\shell\open\command "(Default)" = "%UserProfile%\Local Settings\Application Data\pw.exe" /START "%1" %*
HKEY_CLASSES_ROOT\pezfile\shell\open\command "(Default)" = "%UserProfile%\Local Settings\Application Data\pw.exe" /START "%1" %*
HKEY_LOCAL_MACHINE\SOFTWARE\Clients\StartMenuInternet\FIREFOX.EXE\shell\open\command "(Default)" = "%UserProfile%\Local Settings\Application Data\pw.exe" /START "C:\Program Files\Mozilla Firefox\firefox.exe"
HKEY_LOCAL_MACHINE\SOFTWARE\Clients\StartMenuInternet\FIREFOX.EXE\shell\safemode\command "(Default)" = "%UserProfile%\Local Settings\Application Data\pw.exe" /START "C:\Program Files\Mozilla Firefox\firefox.exe" -safe-mode
HKEY_LOCAL_MACHINE\SOFTWARE\Clients\StartMenuInternet\IEXPLORE.EXE\shell\open\command "(Default)" = "%UserProfile%\Local Settings\Application Data\pw.exe" /START "C:\Program Files\Internet Explorer\iexplore.exe"
HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Security Center "AntiVirusOverride" = "1"
HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Security Center "FirewallOverride" = "1"

Sunday, May 1, 2011

Remove Win 7 Anti-Virus 2011 Counterfeit and Parasite

The program is a half-counterfeit and a half-parasite.It reports merely invented system problems. That provides a ground for its determination as a counterfeited system improver.
Further on, Win 7 Anti-Virus 2011 comprises totally free scanners that actually detect system problems, but there are two problems in such utilization, luck of authorization of  the free scanners developers and poor quality of such tools. It should be emphasized that the tools  applied by Win 7 Anti-Virus 2011 in violation to their owners rights do not pretends to provide exhausting system protection. They often fail to recognize a good half of threats and in overwhelming majority of cases are useless against  latest releases of computer infections.
If genuine scanners fail do detect adequate number of infections, the adware will add intentional false positives to prove the system is in danger and thus provide a reason for its paid activation.
Even the threats that have been actually detected will not be cured, if you activate the counterfeit.
Get rid of Win 7 Anti-Virus 2011 as inappropriate and illegal software product. Click here to apply best quality free scanner for the purpose of Win 7 Anti-Virus 2011 removal.

Win 7 Anti-Virus 2011 screenshot:


Rogue anti-spyware removal tool:


Win 7 Anti-Virus 2011 manual removal guide:
Delete infected files:
 %UserProfile%\AppData\Local\pw.exe
%UserProfile%\AppData\Local\MSASCui.exe
%UserProfile%\Local Settings\Application Data\pw.exe
%UserProfile%\Local Settings\Application Data\MSASCui.exe

Delete Win 7 Anti-Virus 2011 registry entries:
 HKEY_CURRENT_USER\Software\Classes\pezfile
HKEY_CLASSES_ROOT\pezfile
HKEY_CURRENT_USER\Software\Classes\.exe\shell\open\command "(Default)" = "%UserProfile%\Local Settings\Application Data\pw.exe" /START "%1" %*
HKEY_CURRENT_USER\Software\Classes\pezfile\shell\open\command "(Default)" = "%UserProfile%\Local Settings\Application Data\pw.exe" /START "%1" %*
HKEY_CLASSES_ROOT\.exe\shell\open\command "(Default)" = "%UserProfile%\Local Settings\Application Data\pw.exe" /START "%1" %*
HKEY_CLASSES_ROOT\pezfile\shell\open\command "(Default)" = "%UserProfile%\Local Settings\Application Data\pw.exe" /START "%1" %*
HKEY_LOCAL_MACHINE\SOFTWARE\Clients\StartMenuInternet\FIREFOX.EXE\shell\open\command "(Default)" = "%UserProfile%\Local Settings\Application Data\pw.exe" /START "C:\Program Files\Mozilla Firefox\firefox.exe"
HKEY_LOCAL_MACHINE\SOFTWARE\Clients\StartMenuInternet\FIREFOX.EXE\shell\safemode\command "(Default)" = "%UserProfile%\Local Settings\Application Data\pw.exe" /START "C:\Program Files\Mozilla Firefox\firefox.exe" -safe-mode
HKEY_LOCAL_MACHINE\SOFTWARE\Clients\StartMenuInternet\IEXPLORE.EXE\shell\open\command "(Default)" = "%UserProfile%\Local Settings\Application Data\pw.exe" /START "C:\Program Files\Internet Explorer\iexplore.exe"
HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Security Center "AntiVirusOverride" = "1"
HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Security Center "FirewallOverride" = "1"

Saturday, April 30, 2011

XP Anti-Spyware 2011 Removal for PC Independence

Hackers issue viruses. Many IT experts dedicate themselves to preventing   virus mass-spreading. However, the current solution is a PC specific protection, because the web provides great liberties for swindlers to block viruses before approaching computer systems. PC specific protection means a security solution (antiviris) is to be installed on a PC or else the PC is vulnerable to viruses.
Some of the swindlers have invented other viruses in that connection. XP Anti-Spyware 2011 is one of such recent viruses, which pretend to replace a protection for computer system. However, it should not be confused with a mere fake antivirus.
A fake antivirus is only aimed on faking security solution to be rewarded as though it is providing security services. In case of the rogue in question, the scam goes beyond as the counterfeiting has become a secondary purpose of the adverting infection introduction. The aim is to keep genuine security tools off a compromised machine and thus to turn such machine into a bot governed by remote hackers.
Get rid of XP Anti-Spyware 2011 to prevent your PC from becoming a slave to hackers. XP Anti-Spyware 2011 removal tool and free scanner is ready for download here. The link is ban-protected. If any difficulties occur in the course if using the link, please restart your PC is Safe Mode with Networking (tip for Windows XP users) and try again.

XP Anti-Spyware 2011 screenshot:


XP Anti-Spyware 2011 remover download:


XP Anti-Spyware 2011 manual removal instructions:
Delete infected files:
%UserProfile%\AppData\Local\pw.exe
%UserProfile%\AppData\Local\MSASCui.exe
%UserProfile%\Local Settings\Application Data\pw.exe
%UserProfile%\Local Settings\Application Data\MSASCui.exe
Delete infected registry entries:
HKEY_CURRENT_USER\Software\Classes\pezfile
HKEY_CLASSES_ROOT\pezfile
HKEY_CURRENT_USER\Software\Classes\.exe\shell\open\command "(Default)" = "%UserProfile%\Local Settings\Application Data\pw.exe" /START "%1" %*
HKEY_CURRENT_USER\Software\Classes\pezfile\shell\open\command "(Default)" = "%UserProfile%\Local Settings\Application Data\pw.exe" /START "%1" %*
HKEY_CLASSES_ROOT\.exe\shell\open\command "(Default)" = "%UserProfile%\Local Settings\Application Data\pw.exe" /START "%1" %*
HKEY_CLASSES_ROOT\pezfile\shell\open\command "(Default)" = "%UserProfile%\Local Settings\Application Data\pw.exe" /START "%1" %*
HKEY_LOCAL_MACHINE\SOFTWARE\Clients\StartMenuInternet\FIREFOX.EXE\shell\open\command "(Default)" = "%UserProfile%\Local Settings\Application Data\pw.exe" /START "C:\Program Files\Mozilla Firefox\firefox.exe"
HKEY_LOCAL_MACHINE\SOFTWARE\Clients\StartMenuInternet\FIREFOX.EXE\shell\safemode\command "(Default)" = "%UserProfile%\Local Settings\Application Data\pw.exe" /START "C:\Program Files\Mozilla Firefox\firefox.exe" -safe-mode
HKEY_LOCAL_MACHINE\SOFTWARE\Clients\StartMenuInternet\IEXPLORE.EXE\shell\open\command "(Default)" = "%UserProfile%\Local Settings\Application Data\pw.exe" /START "C:\Program Files\Internet Explorer\iexplore.exe"
HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Security Center "AntiVirusOverride" = "1"
HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Security Center "FirewallOverride" = "1"

Trojan.Win32.Monderb Removal Technology

Trojan.Win32.Monderb is a program written on  C++. It is compatible with Windows and other operating system, with Windows as a primary target.
 The infection is  installed in a way that is referred to by IT experts as obfuscation. Obfuscation implies tricks aimed to conceal the infection and thus to reduce Trojan.Win32.Monderb removal risk.
The trojan in question practices  deletion of its original entry which is dropped into system folder under random name. By the way, random name also proves the intention of the trojan to bewilder  potential Trojan.Win32.Monderb removers.
The original entry is deleted once it succeeds to create subsequent  morph of the trojan. New created version of the trojan  performs a set of destructive actions and tends to migrate, i.e. to change its system address.
Get rid of Trojan.Win32.Monderb in spite of its self-defense tricks, as well as clean your PC of other parasites applying free scanner available here

Trojan.Win32.Monderb variants:
Trojan.Win32.Monderb [Ikarus]
Trojan.Win32.Monderb.acke
Trojan.Win32.Monderb.ahoe
Trojan.Win32.Monderb.almg
Trojan.Win32.Monderb.aprm
Trojan.Win32.Monderb.gen
Trojan.Win32.monderb.gjo
Trojan.Win32.Monderb.gjb
Trojan.Win32.Monderb.kuf
Trojan.Win32.Monderb.vwm
Trojan.Win32.Monderb.yek
Trojan.Win32.Monderb.yfa

Trojan.Win32.Monderb remover download:


Remove Antivirus Center Scareware – AntivirusCenter Remover

Antivirus Center (AntivirusCenter) is a software product that hails from the labs of experienced rascals. They employ a good many web-promoters, both automated and human spammers and flooder, to introduce as many copies of the scareware as possible.
The program in question as  a scareware  tool as it generates messages related to computer security without any security activities to be taken by genuine security solution. The messages  are of the same kind regardless of  PC they pretend to describe. The main idea of them is that system needs critical treatment by security software or else it will be badly corrupted.
Some of the alerts, to look more convincing, are   shown in windows resembling system windows. The adware may also try to bewilder users applying expressions like “Windows recommend to active the critical update” (referring to Antivirus Center).
Windows would recommend to get rid of Antivirus Center immediately, if it were of any opinion on this software. Click here to waste no more time and launch Antivirus Center removal initiating free scan

Antivirus Center screenshot:


Antivirus Center removal tool:

Antivirus Center manual removal guide:
Delete infected files:

%AllUsersProfile%\Application Data\[random].dat
%AllUsersProfile%\Application Data\[random].ico
%UserProfile%\Application Data\Microsoft\Internet Explorer\Quick Launch\Antivirus Center.lnk
%UserProfile%\Desktop\Antivirus Center.lnk
%Temp%\ins2.tmp
%Temp%\mv3.tmp
%Temp%\wrk4.tmp

Delete infected registry entries:

HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Services\SharedAccess\Parameters\FirewallPolicy\StandardProfile\AuthorizedApplications\List “C:\WINDOWS\system32\rundll32.exe” = ‘C:\WINDOWS\system32\rundll32.exe:*:Enabled:Antivirus Center’
HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Run “[random]“


Thursday, April 28, 2011

Remove "System plugin at address 0x00874324 got critical error" popup

If any popup requests you to dial a number, it is a sure sign of  trickery. Such popups are generated by special kind of trojans classified as ransomware (ransom claiming software). To get rid of the popups users concerned need to exterminate relevant trojans.
Recent striking example of ransomware is a popup talking nonsense about plugin error which you need to deactivate dialing one of the numbers it specifies. The numbers have proven to be a premium rate overseas number. According to the popup, you need to call one of the number for deactivation code.
To get rid of "System plugin at address 0x00874324 got critical error" popup and unlock your PC, please try to enter the following crack into the relevant fields of the popup: 27496.
If that has not eliminated the popup, you need to get your system into Safe Mode with Networking. This mode is available in Windows boot menu. To enter the menu, press F8 on reboot.
To complete removal of "System plugin at address 0x00874324 got critical error" issue, click here to run free scan and  get rid of trojan generating  the popup. 

System plugin at address 0x00874324 got critical error screenshot:


Download Spyware Doctor:

"System plugin at address 0x00874324 got critical error" manual removal guide:
Delete infected files:
C:\ProgramData\svchost.exe
C:\ProgramData\delself.bat
C:\ProgramData\svchost.tmp_time
Delete infected registry entries:
HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Winlogon "Userinit= "

Get Rid of Trojan.Win32.Scar.coye or Related Parasites

Trojan.Win32.Scar.coye is a variant of   generic trojan related to sham security solutions  for Windows computer systems and denial of services attacks. However, its payload is not a constant  substance  as the trojan establishes a backdoor connection and listens to remote server. It downloads, at least relevant attempts are made, content specified in the messages it receives from the remote server.
Observations have revealed its habit of deleting its body after downloading more complex threat which payload repeats and extends the trojan original tasks.
Trojan.Win32.Scar.coye removal is therefore to be completed by its related components extermination and/or detection, even if the detection is negative.
Click here to get rid of Trojan.Win32.Scar.coye, otherwise known as Trojan:Win32/Kolbot.A, Win-Trojan/Bypassagent.41984.J, Mal/Generic-L, as well  detect and exterminate malicious content it drops into victimized PC. 


Trojan.Win32.Scar.coye remover: